TL;DR
Uber says a third-party provider’s compromised internal credentials were used to access Uber data held with that provider. Uber confirmed to TechCrunch that the provider was Fireworks.ai; reporting by TechCrunch says driver’s license information was among the data taken. The number affected nationwide and the data involved for each recipient remain unclear.
Uber is notifying people that their personal information was accessed through a security incident at vendor Fireworks.ai, after the provider’s compromised internal credentials were used to reach an Uber account it held. TechCrunch reported on November 13 that breach notices it reviewed included driver’s license information; the public sample notice does not specify which data was involved for each recipient.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
In a notice dated November 10, 2026, Uber said a service provider told it on October 9 that an unauthorized party had compromised the provider’s internal credentials and used them to access Uber’s account with the provider. Uber said it cut the data connections and investigated. By October 13, the company had determined that the credentials had been used to access Uber data connected to the provider.
Uber’s notice filed with the California attorney general does not name the vendor. An Uber spokesperson identified it as Fireworks.ai in comments to TechCrunch, saying the vendor had access to some Uber data. Fireworks also confirmed to the outlet that it had identified unauthorized access to some of its systems affecting customer data. The available accounts describe access through the provider relationship; they do not say that the intruder entered Uber’s own systems.
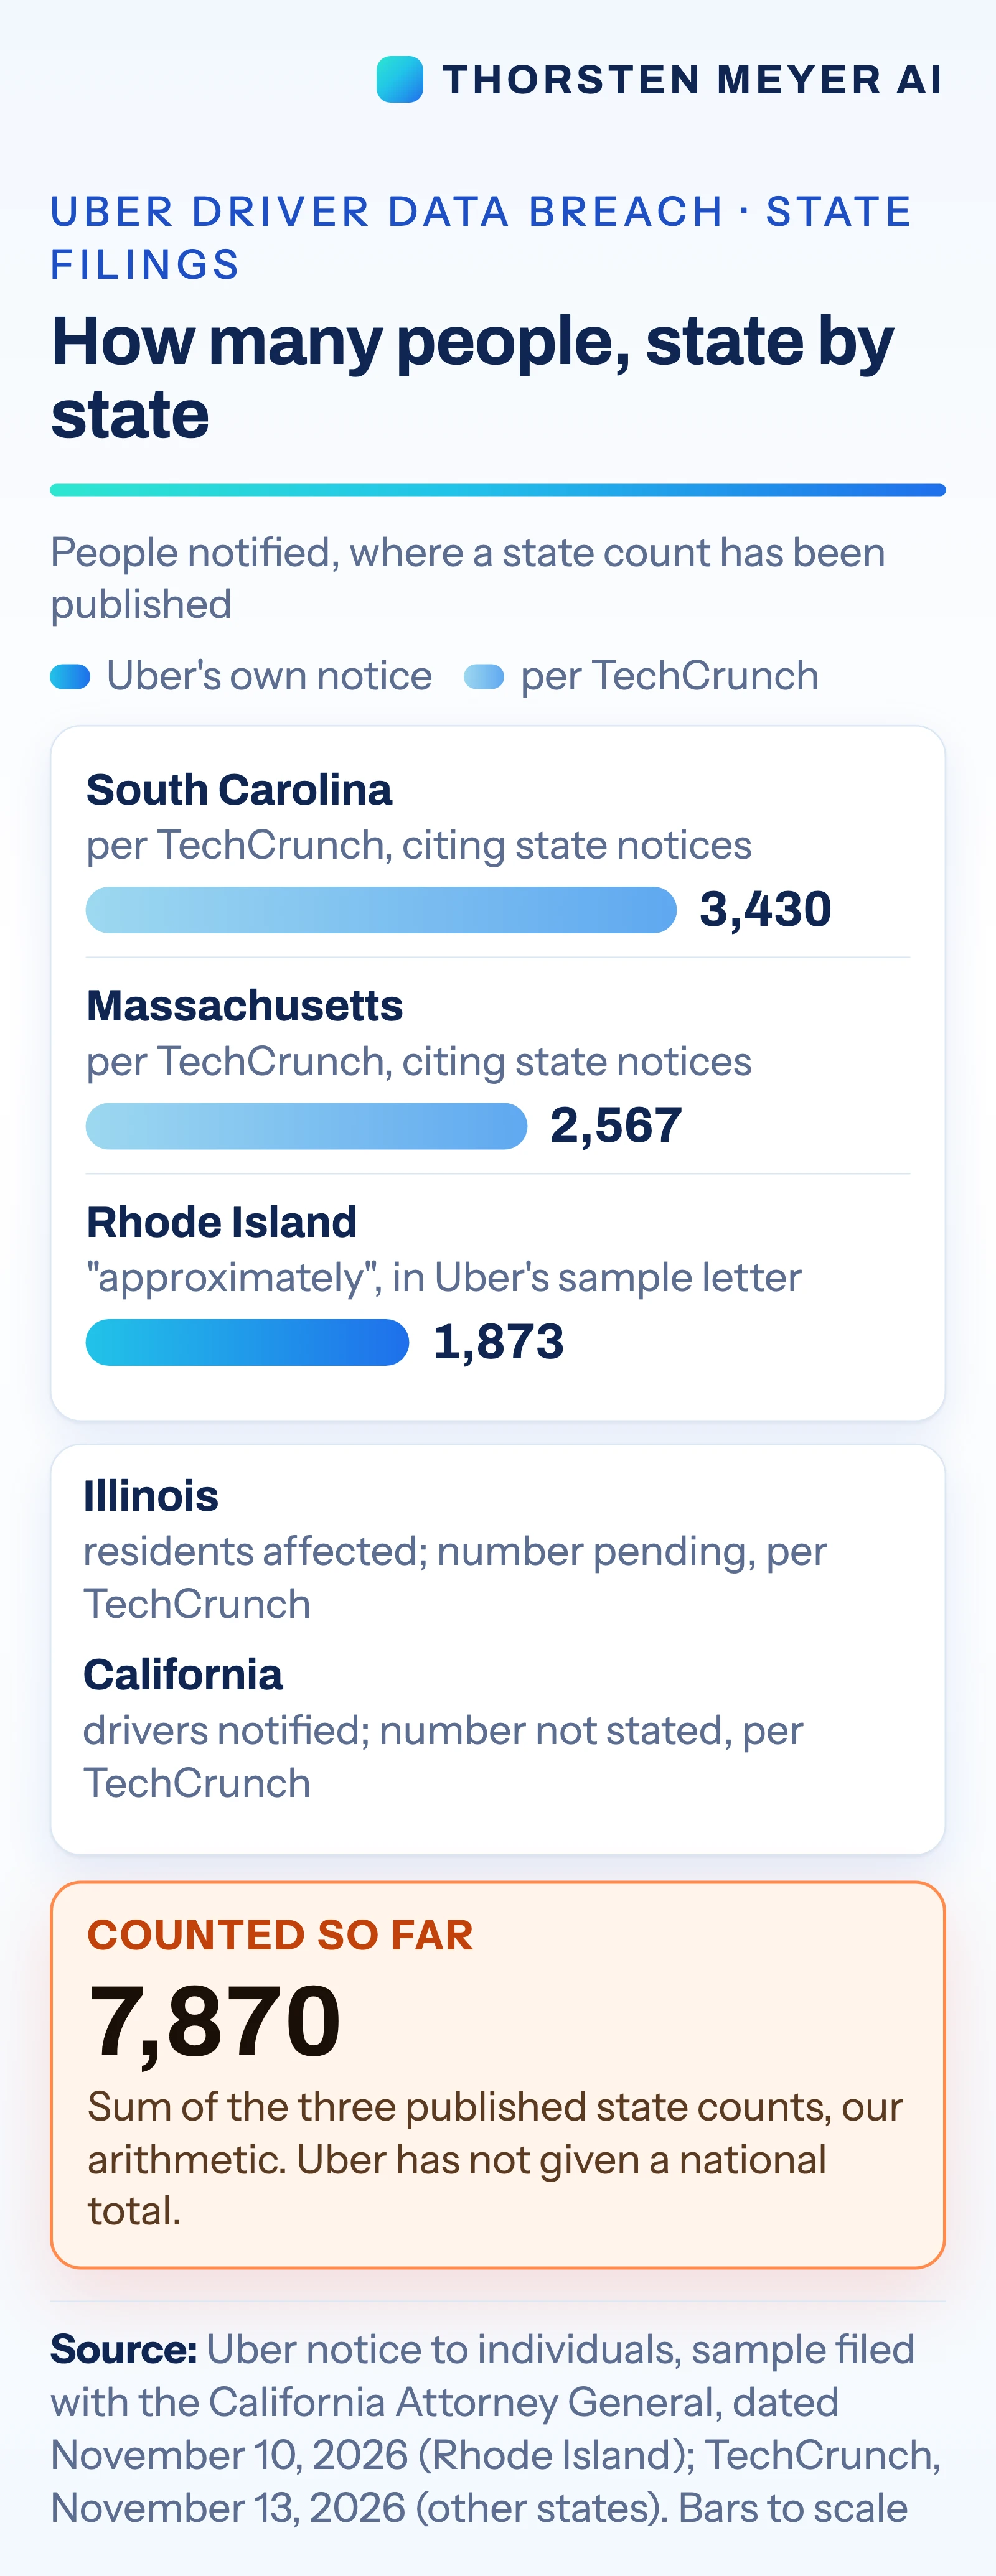
The public sample letter leaves the field describing affected information blank. TechCrunch says the individual notices it reviewed included driver’s license information, but recipients need to consult their own letters to see what information Uber says was involved in their case. Uber’s notice lists about 1,873 Rhode Island residents. TechCrunch reported 2,567 people in Massachusetts and 3,430 in South Carolina. Those three state counts total 7,870, but no national total is available in the supplied reports.
Why License Data Raises Concern
For affected drivers, the reported inclusion of driver’s license information makes the notices more consequential than a general warning about an account or service disruption. A license contains identifying details, and its exposure can create a risk of attempted fraud or identity misuse. The sources do not establish that anyone has used the accessed information for those purposes.
Uber says it has not identified any misuse to date. That is the company’s assessment at the time of its notice, not a guarantee that misuse cannot occur later. The incident also highlights that information shared with a service provider can be exposed through that provider’s systems, even when the notice does not describe a breach of Uber’s own systems.
The reported state figures offer only a partial view. They show that people in at least three states were counted in notices or filings, but they do not establish the full number of affected people or whether the same types of information were involved for every recipient. Readers should treat the letter addressed to them as the source for their own reported exposure.
Products Worth Considering

Anker SOLIX C1000 Gen 2 Portable Power Station with 100W Solar Panel

Apple Watch Ultra 4 GPS + Cellular, 49 mm

Anker SOLIX C300 DC Portable Power Station with 60W Solar Panel, 288Wh, 300W
As an affiliate, we earn on qualifying purchases.
How the Vendor Link Worked
Fireworks AI provides a platform for businesses to run and customize open AI models. The connection to Uber matters because the incident described by Uber involved credentials held inside the service provider and an Uber account there. The available reporting does not detail what Uber data was stored through the connection or why the vendor needed each category of information.
Fireworks’ security bulletins say the company identified unauthorized use of internal credentials on October 6, Pacific time. The bulletins state that an unauthorized party accessed environment variables used in evaluation jobs in a limited number of customer accounts, and that Fireworks began notifying affected customers on October 7. Uber’s filing lists October 7 as the breach date, while its notice says the provider contacted Uber on October 9. These dates refer to different reported steps in the incident and notification timeline.
Uber’s notice says it severed data connections after the October 9 alert and determined on October 13 that Uber data had been accessed. The notice was dated November 10, the same date Uber reported the incident to California. TechCrunch reported the license information and Uber’s identification of Fireworks on November 13. Reuters, which also reviewed the California filing, reported that the notice did not name the provider or list the data involved.
““an unauthorized third party had compromised the service provider’s internal credentials and used them to access Uber’s account with the service provider.””
— Uber, in its security incident notice
What Each Notice Will Specify
The public sample letter does not identify the specific information involved, and the available material does not establish whether every recipient’s data included a license number. TechCrunch’s account is based on notices it reviewed; each recipient should check their own letter for the data field completed for them.
The total number of affected people nationwide has not been stated in the supplied reports. The three state counts cannot be treated as a complete tally. The sources also do not say what the accessed data was used for, identify the unauthorized party, or report confirmed misuse. Fireworks’ statements about the affected customer accounts do not provide a full account of which Uber records were accessible.
Check the Letter and Enroll
Uber says affected people can receive free credit monitoring and fraud assistance through Cyberscout, a TransUnion company. Enrollment must take place within 90 days of the date on the letter. Recipients should check the letter for the information Uber says was accessed, the enrollment instructions, and the applicable deadline.
The materials also refer to credit reports, fraud alerts, and freezes as available steps associated with the response. The supplied information does not set out instructions for those options or say that a particular step is required for every recipient. Uber’s notice says it cut the provider’s data connections and investigated; further details about the affected population, the data accessed, or any later finding of misuse have not been provided here.
Key Questions
Was Uber’s own system breached?
Uber’s notice says compromised service provider credentials were used to access Uber data connected to the provider. It does not describe an intrusion into Uber’s own systems.
Was driver’s license information exposed?
TechCrunch reported that the notices it reviewed included driver’s license information. The public sample letter leaves the affected-data field blank, so recipients should check their own notice to see what information Uber lists for them.
How many people were affected?
Uber’s notice lists about 1,873 Rhode Island residents. TechCrunch reported 2,567 in Massachusetts and 3,430 in South Carolina. The available sources do not give a national total.
What assistance does Uber offer?
Uber says recipients can enroll in free credit monitoring and fraud assistance through Cyberscout, a TransUnion company. Enrollment is due within 90 days of the date on the recipient’s letter.
Has Uber reported confirmed misuse?
Uber said it had not identified misuse to date. The available reports do not establish what the accessed data was used for or whether misuse may be identified later.
Source: Thorsten Meyer AI